Security Operations Center with an AI Analyst
An open-source security operations center that detects and responds to attacks, with an AI analyst that takes no action without human approval.
Case studySecurity monitoring, threat detection, digital forensics and system protection.
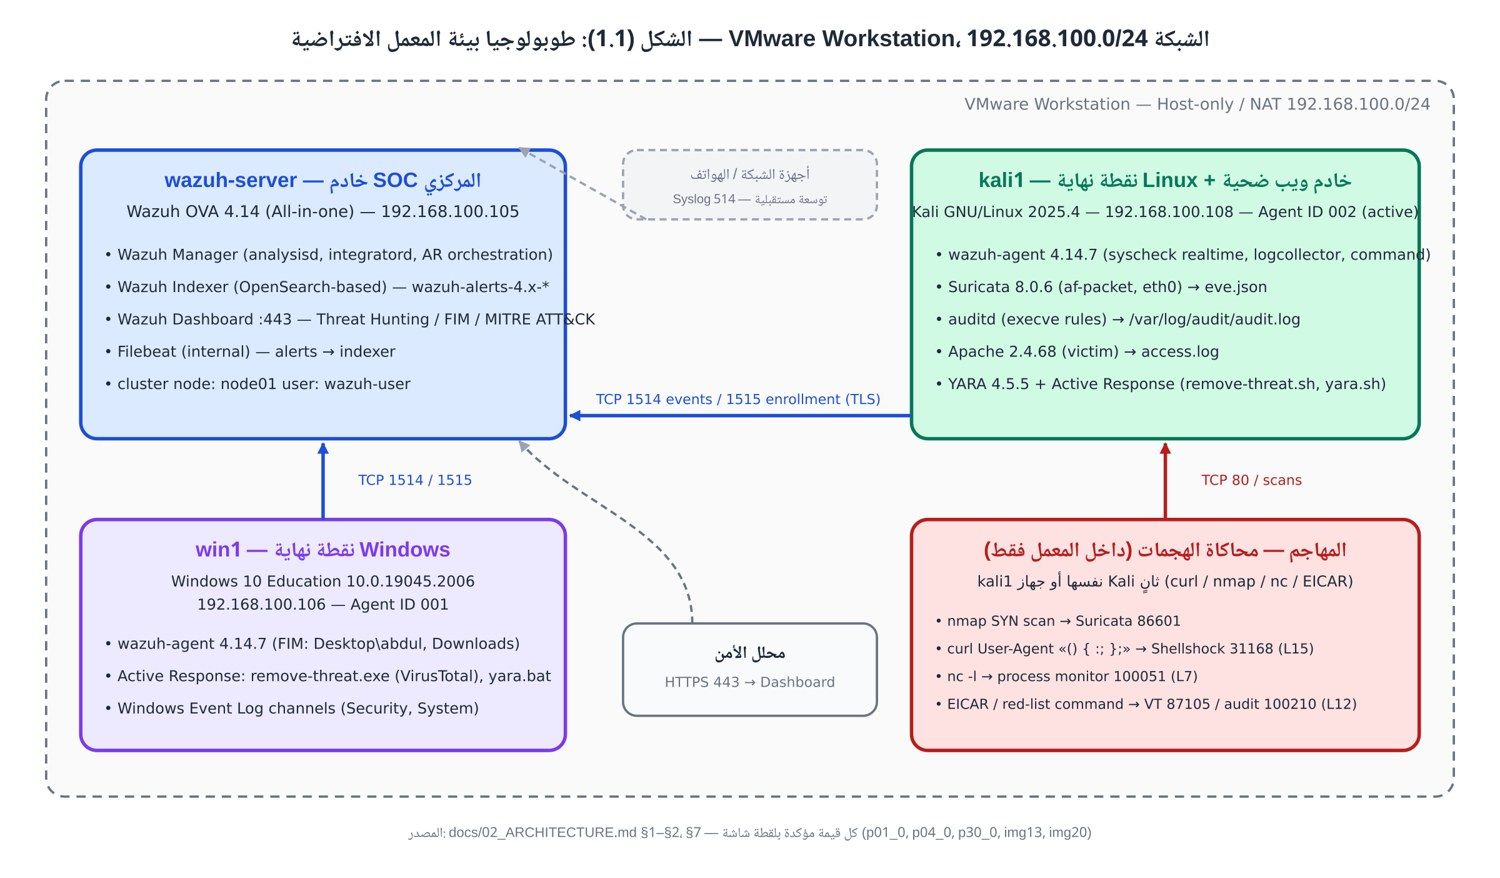
Security is not a product you buy once; it is continuous monitoring and response. We build monitoring that detects attacks early and connect it to a controlled automatic response that blocks nothing without a clear rule or human approval.
When an incident happens, we analyse and document the digital evidence in a report that shows exactly what happened. And we assess your applications so you know their weaknesses before someone else does.
Threat monitoring and detection, controlled automatic response and documented use cases.
Evidence analysis and documentation, with a detailed incident report.
Installing and tuning protection systems, with documented configuration.
Vulnerability analysis and a security report with remediation guidance.
Detect attacks early, before they reach your data.
Know exactly what happened in any incident, with documented evidence.
Protects your network from breaches and suspicious traffic.
Find your app's weak points before someone else does.
We assess applications and systems only under a written agreement that defines scope and authority, and never test without explicit authorisation.
We design it with protected allow-lists and parameters taken from the incident itself; sensitive actions need human approval and every action is logged.
Tell us what you need in two lines and we will reply with the next step.
Tell us what you need in two lines and we will reply with the next step.
Message us on WhatsApp